14–16 October 2026 · Paris, France
4th European Health Data Protection Congress
Protecting Health Data. Enabling Innovation. Building Trust.
Three days bringing together regulators, hospitals, pharmaceutical and biotech companies, research institutions, technology leaders, Data Protection Officers and policy-makers around one question: how can Europe unlock the value of health data while maintaining trust, privacy, security and regulatory compliance?
Secure your spotSpeaker confirmed All times are Paris time (CEST) · programme subject to change
Day 1 — Wednesday 14 October 2026
The new regulatory landscape
Congress opening
Opening remarks and strategic outlook on the future of health data governance in Europe and globally.
 Opening
Pierre-Yves Lastic,
EFDPO / EHDPC
Secretary General; EHDPC Chairman
France
Pierre-Yves Lastic is Secretary General of EFDPO and Chairman of EHDPC. He has worked in pharmaceutical data management, clinical research and privacy for nearly three decades, including senior privacy leadership roles at Sanofi. He established Sanofi's Global Privacy Office and has been active in European data protection organisations.
Revolution or evolution in health data protection?
Focus · Guidelines 1/2026 on the processing of personal data for scientific research purposes
The health data ecosystem is undergoing unprecedented transformation. New regulations, technological breakthroughs and increasing societal expectations are reshaping the way organisations collect, share and protect health information.
This session will examine whether Europe is witnessing a regulatory revolution or a natural evolution of existing governance models, and what this means for healthcare organisations, researchers and innovators.
Introductory presentations (30 min) followed by a 45-minute panel discussion.
Co-chair
Pierre-Yves Lastic,
EFDPO / EHDPC
Secretary General; EHDPC Chairman
France
Pierre-Yves Lastic is Secretary General of EFDPO and Chairman of EHDPC. He has worked in pharmaceutical data management, clinical research and privacy for nearly three decades, including senior privacy leadership roles at Sanofi. He established Sanofi's Global Privacy Office and has been active in European data protection organisations.
 Co-chair
Giuseppe D’Acquisto,
Garante (Italian DPA)
Senior Technology Policy Adviser
Italy
Giuseppe D’Acquisto is Senior Technology Policy Adviser
at the Italian Data Protection Authority. He represents Italy
in the EDPB Technology Expert Group and the International
Working Group on Data Protection in Technology, and serves as
the EDPB representative on artificial intelligence in the
Digital Markets Act High-Level Group. He teaches Artificial
Intelligence and Laws and Algorithms at LUISS University in
Rome and holds a degree in electronic engineering and a PhD in
computer science.
 Panellist
Donovan Sheppard,
UCB
Head of Data Protection Advisory & DPO
Belgium
Donovan Sheppard is Head of Data Protection Advisory and
Data Protection Officer at UCB, where he leads the global
team helping the company use data responsibly across clinical
research, healthcare innovation, HR, digital solutions and
commercial activities. A lawyer with more than a decade of
privacy and data protection experience, he is CIPP/E
certified and a GDPR Auditor. He advises on the responsible
use of health data and emerging technologies, connecting
legal requirements, business objectives and patient
expectations.
 Panellist
Sarah Maalej,
Aix-Marseille Université
Data law counsel, CEDRE project
France
Sarah Maalej is a data law counsel and project officer for
CEDRE at Aix-Marseille Université, where she supports
research data governance and the responsible use of research
data.
The Biotech Act and Europe’s innovation agenda
Europe’s ambition to remain globally competitive in life sciences depends on its ability to foster innovation while ensuring robust safeguards for patients and citizens.
This session will explore how the Biotech Act may influence research, investment, innovation and international competitiveness within the healthcare and pharmaceutical sectors.
Introductory presentation followed by a panel discussion.
 Co-chair · Keynote
Kristof Van Quathem,
Covington & Burling
Of Counsel
Belgium
Kristof Van Quathem is Of Counsel in Covington's Brussels office. He advises organisations on EU data protection, cybersecurity and digital regulation, including the GDPR, AI Act, Data Act and European Health Data Space, with a focus on life sciences and technology.
 Panellist
Marta Siemaszko,
Novartis
Global Operations Director, Data Privacy, Digital and
AI
Poland
With over 15 years of experience in the healthcare and
pharmaceutical sectors, Marta Siemaszko focuses on integrating
privacy governance and ethical AI into Novartis global
operations. Her work supports Global Drug Development, Patient
Safety and Quality Assurance, and includes strategic advice on
data governance, anonymisation and the secondary use of health
data. She holds a Master of Law and the CIPP/E, CIPM and AIGP
certifications, and chairs the GDPR Working Group at INFARMA,
the Polish affiliate of EFPIA.
 Panellist
Sue Foster,
AstraZeneca
Senior Director, Clinical Technologies Privacy & Data
Risk
United Kingdom
Sue Foster is Senior Director, Clinical Technologies Privacy
& Data Risk at AstraZeneca. Her work focuses on helping
sponsors of global clinical studies align technology systems
and organisational processes with local privacy and clinical
regulatory requirements, including the interaction between AI
and privacy. Previously in private legal practice for more
than two decades, she is qualified in England and Wales and
California and holds CIPP/E and AIGP certifications. She
represents AstraZeneca in the EFPIA Data Governance Working
Group and IPMPC working groups.
Oral communications session
 Chair
Marie Penot,
EuroDataProtection UG
Founder and Consultant
Germany
Marie Penot is the founder and a consultant at
EuroDataProtection UG, where she advises organisations on GDPR
compliance and data protection across European markets.
Six 10-minute oral communications. Abbie Pratt will present two abstracts in one slot (5 minutes each).
-
RWD, Secondary Use and Anonymisation: Is this a Legal or a Policy Issue?SB Speaker Stefano Biondi, Menarini Group Data Protection Officer Florence, Italy Stefano Biondi is Group Data Protection Officer at Menarini. His oral communication examines whether the governance of real-world data, secondary use and anonymisation should be treated primarily as a legal issue or as a policy issue.
-
Secondary Use of Clinical Trial Data: Has the Law Become Clearer?
 Speaker
Pippa Parker,
The DPO Centre
Data Protection Officer
London, United Kingdom
Pippa Parker is a Data Protection Officer at The DPO Centre. Her presentation reviews how recent case law and EDPB and ICO guidance on anonymisation, pseudonymisation and scientific research affect the secondary use of clinical-trial data in real-world scenarios.
-
From Months to Days: Systematising Dataset Generation to Reduce the Information Governance Burden
 Speaker
Diana Molchanova,
Softwire Technology Limited
Software Developer
London, United Kingdom
Diana Molchanova is a software developer at Softwire Technology Limited. Her case study with two ophthalmology institutions presents a standardised, auditable approach to data classification, anonymisation and dataset generation that reduced delivery time from months to days.
-
Synthetic Imaging in Cross-Border Virtual Tumour Boards: Uses and Limitations
 Speaker
Pablo Suriol,
Sciensano
Scientist
Brussels, Belgium
Pablo Suriol is a scientist at Sciensano. His oral communication examines synthetic imaging for cross-border virtual tumour boards, addressing practical use cases, limitations, GDPR and EHDS requirements, anonymisation and residual re-identification risks.
-
5 min each What Evidence Do Healthcare Organizations Need to Evaluate Proprietary Artificial Intelligence Systems? When Should Operational Workflow Changes Trigger Reassessment of an Unchanged Clinical Artificial Intelligence Model?
 Speaker
Abbie Pratt,
Elite Advantage
Healthcare Technology Executive & AI Governance Advisor
Chicago, United States
Abbie Pratt is a healthcare technology executive and AI governance advisor at Elite Advantage. Her two communications address the minimum evidence healthcare organisations need to evaluate proprietary clinical AI and the workflow or input changes that should trigger reassessment of an unchanged model.
-
Data Completeness in Healthcare AI: Definitions, Requirements and Policy Recommendations
 Speaker
Elisabetta Biasin,
KU Leuven Centre for IT & IP Law
Researcher in Law
Leuven, Belgium
Elisabetta Biasin is a legal researcher at KU Leuven’s Centre for IT & IP Law whose work covers data protection, cybersecurity, artificial intelligence and health data. Her presentation explores data completeness under Article 10(3) of the AI Act and proposes healthcare-specific assessment metrics.
The Digital Omnibus
The Digital Omnibus package reopens parts of the European digital rulebook, from AI Act deadlines to transparency obligations. This session unpacks what changes, what stays, and what health data controllers should be doing now.
16:30–17:30. Introductory presentations (15 min) followed by a 45-minute panel discussion.
 Co-chair
Winnie Dongbou Wamba,
MyData-TRUST
Transformation Lead & Senior Data Protection Lawyer
Belgium
Winnie Dongbou Wamba is a senior data protection lawyer
specialising in the life sciences sector, with experience
advising on global privacy, health data research and
cross-border data transfer matters. He is currently pursuing a
PhD in law on the legal and ethical challenges of synthetic
data in research, with a particular focus on clinical research
and the European Health Data Space. His work sits at the
intersection of data protection, medical law, emerging
technologies and research ethics.
 Keynote
Valda Beizitere,
European Commission
Legal and Policy Officer
Brussels, Belgium
Valda Beizitere is a Legal and Policy Officer at the European
Commission in Brussels.
 Panellist
Natalie Stockmann,
Ascensia Diabetes Care
Data Protection Officer, PHC Group Europe
Switzerland
Natalie is Data Protection Officer for the European companies
in the PHC Group, including Ascensia Diabetes Care. In this
role, Natalie heads the Data Privacy Office and advises on
data-, AI- and cybersecurity related legal and policy matters
globally (outside Japan). Prior to joining, she was Data
Protection Officer and General Counsel at a tech
scale-up.
 Panellist
Nathalie Poupaert,
Fieldfisher
Counsel, Technology & Data
Belgium
Nathalie Poupaert is Counsel in Fieldfisher's Technology & Data practice. She advises on GDPR, ePrivacy, AI and digital health, including cross-border data transfers, incident response and health-data governance. She also acts as an external Data Protection Officer.
Oral communications session
 Chair
Anne Bahr,
Sanofi
R&D Privacy Officer
France
Anne Bahr is R&D Privacy Officer in Sanofi’s
Global Privacy Office. She supports research and
development projects involving health data, including
real-world data studies, registries, managed access
programmes, patient support programmes and data
foundations. Her earlier work covered worldwide clinical
studies and international R&D projects, with a focus
on patient consent, ethics review, biological samples,
secondary use and anonymisation. She represents Sanofi in
the EFPIA Data Governance Working Group, is CIPP/E
certified and holds a PhD in Molecular Biology.
16:30–17:40. Seven 10-minute oral communications.
-
Five Perspectives on EHDS Transparency, Data Access and Re-identification Risk
 Speaker
Xiao Liu,
European Organisation for Research and Treatment of Cancer (EORTC)
Data Protection Officer
Brussels, Belgium
Xiao Liu is Data Protection Officer at the European Organisation for Research and Treatment of Cancer. Her five submissions examine EHDS transparency, sustainable access to research data, re-identification risk in molecular data, quasi-identifiers in oncology and the context-dependent nature of anonymisation.
-
Genuinely Scientific or Innovative Research? Unpacking the Relevance of “Scientific Research” Exemptions in the European Union’s Legal Landscape
 Co-speaker
Marta Musidlowska,
Ghent University
PhD Researcher
Ghent, Belgium
Marta Musidlowska is a PhD researcher at Ghent University whose work focuses on privacy and data protection in healthcare, including the secondary use of health data. With Griet Verhenneman, she examines legal uncertainty around what qualifies as genuinely scientific or innovative research under the EHDS, EDPB guidance and the Biotech Act.
 Co-speaker
Griet Verhenneman, PhD,
Ghent University
Assistant Professor
Ghent, Belgium
Griet Verhenneman is an Assistant Professor at Ghent University with a research focus on privacy and data protection in healthcare. With Marta Musidlowska, she proposes a risk-based approach to the scientific-research exemptions and the legal uncertainty created by overlapping European health-data rules.
-
The “Same Controller” Restriction: The Draft Biotech Act’s Impact on Industry
 Speaker
Lawrence Carter,
The DPO Centre
Data Protection Officer
London, United Kingdom
Lawrence Carter is a Data Protection Officer at The DPO Centre. His presentation examines the draft Biotech Act’s proposed “same controller” restriction and its practical consequences for reusing clinical-trial data, including sponsorship, access and controller roles.
-
From Sensitive Data to Trusted Genomic Data Infrastructures: How to Enable Responsible Democratic Health Data Governance
 Speaker
Joke Sas,
Sciensano
Scientist
Brussels, Belgium
Joke Sas is a scientist at Sciensano working on the ethical, legal and social aspects of data governance. Her presentation treats genomic data as lifelong, identifiable and widely shared, and argues for independent, transparent, interoperable and risk-based governance within the EHDS.
-
Governance Architecture for Artificial Intelligence Integration in Regulated Pharmaceutical SAP Enterprise SystemsRK Speaker Ramesh Kanugula, Sumeru Technologies LLC Technical Architect Chicago, United States Ramesh Kanugula is a Technical Architect at Sumeru Technologies LLC. He presents an AI governance architecture for regulated pharmaceutical SAP environments using role-based access, secure APIs, identity federation, audit logging and transport governance, while preserving human oversight and an advisory role for AI.
-
The Ethics of Innovation: Harmonizing AI, Integrity, and the EHDS
 Speaker
Yves Zieba,
Syntezia Sàrl
Managing Director
Geneva, Switzerland
Yves Zieba is Managing Director of Syntezia Sàrl in Geneva. His oral communication considers the opportunities and risks of artificial intelligence in health, connecting data integrity, explainable AI, interoperability and the European Health Data Space.
-
How Can Healthcare Organisations Prove Compliance When Evidence Depends on External Providers?
Speaker Marie-José Promeneur, La Minute Data Founder & Data Compliance Consultant Paris, France Marie-José Promeneur is the founder of La Minute Data and a data compliance consultant specialising in GDPR, the AI Act and health data. Her presentation explains how organisations can prove compliance when evidence depends on cloud, SaaS and AI providers, focusing on accessibility, validity, scope and availability over time.
To record or not to record: that is the question
Consultation recording, ambient scribes and clinical documentation tools are spreading faster than the guidance that governs them. Supervisory authorities, platform providers and practising clinicians compare positions.
Chair
Marie Penot,
EuroDataProtection UG
Founder and Consultant
Germany
Marie Penot is the founder and a consultant at
EuroDataProtection UG, where she advises organisations on GDPR
compliance and data protection across European markets.
 Panellist
Katharina A. Weimer,
Fieldfisher
Partner · Rechtsanwältin
Germany
Katharina A. Weimer is a partner in Fieldfisher’s
Munich office. She advises national and international clients
on German and European data protection law, with a particular
focus on life sciences, healthcare, clinical research, digital
products and the use of sensitive personal data.
 Panellist
Andrea Hemming,
Tandem Health
General Counsel
Sweden
Andrea Hemming is General Counsel at Tandem Health, where she
leads legal work as the company scales its AI-powered
healthcare products across European markets. Her work covers
health law, privacy, AI regulation, information security,
medical-device regulation and cybersecurity.
 Panellist
Martin Bergman, MD,
Capio Urosurgical Center Stockholm
Urologist, Robotic Surgeon & Medical Director
Stockholm, Sweden
Martin Bergman is a Swedish urologist and robotic surgeon
based in Stockholm. He is Medical Director, founder and CEO of
Capio Urokirurgiskt Centrum Stockholm and has medical
leadership responsibilities across Capio Urology in northern
Stockholm. His clinical work focuses on prostate cancer,
minimally invasive and robotic urologic surgery, specialist-care
pathways, and the responsible integration of digital tools and
health data into everyday clinical practice.
Day 2 — Thursday 15 October 2026
Innovation, risk and operational challenges
Regulatory data protection sandboxes: how they work and what organisations gain from them
What exactly is a regulatory data protection sandbox, how does the process run, and what are the benefits for a company or a healthcare institution taking part in one?
- Legal framework of a regulatory data protection sandbox
- Data protection sandboxes in Europe — overview and comparison
- How the LfDI Rheinland-Pfalz sandbox works, step by step
- First participants in the health area
Interactive segment: what does the audience expect from a sandbox? Which innovations would you submit — or did you shelve because of data protection uncertainty?
 Chair
Nils G. Indahl,
Norwegian Association of DPOs
Chair; DPO, Church of Norway
Norway
Nils G. Indahl is chair of the Norwegian Association of Data
Protection Officers and DPO of the Church of Norway. He holds
a M.Sc. degree in political science from the University of
Copenhagen.
 Speaker
Erik Boucher,
CNIL
Senior health expert engineer
France
Erik Boucher de Crèvecoeur is an information technology
expert at the CNIL, the French data protection authority. With
nearly 30 years of experience in software development, quality
and security management, he is currently involved in the
compliance checking of personal data processing for the French
Health Sector, subject to authorization by the CNIL. As a
representative of the CNIL, he also takes part in several
working groups in charge of defining national data protection
frameworks, as well as international standards for privacy
management, such as ISO/IEC 27701.
 Speaker
Elisabeth Herzog,
LfDI Rheinland-Pfalz
Research Associate, Data Protection Sandbox
Germany
Elisabeth Herzog studied at the universities of Trier and
Bergen. Since 2021, she is a PhD student at Göttingen
University, writing about “Access to Health Data in Germany,
Norway and under the EHDS”, for which she also spent time at
the University of Bergen as a guest researcher. Following
placements at Göttingen University and a law firm in Frankfurt
am Main, she has been working for the project “Die
Datenschutz-Sandbox” at the Authority for Data Protection and
Freedom of Information Rhineland-Palatinate since 2025.
 Speaker
Dr Dieter Kugelmann,
LfDI Rheinland-Pfalz
State Commissioner for Data Protection
Germany
Prof. Dr. Dieter Kugelmann studied at the universities of
Mainz and Dijon. After his Pd.D. in European media law he
qualified at the university of Mainz. He is author of numerous
publications especially on European fundamental rights,
European law, media law, security law and data protection law.
In 2008 he became a fully tenured professor at the German
Police University with a specialization for public law with a
focus on police law including international and European Law.
In 2015 he was elected for President of the Authority for the
protection of data and the freedom of information of
Rhineland-Palatinate and in 2023 he was re-elected for a
second term. He is the editor of a commentary on the data
protection law of Rhineland-Palatinate and co-editor of a
commentary on the GDPR.
 Speaker
Magnus Guldberg Pedersen,
BrainCapture ApS
Machine Learning Researcher and Engineer
Denmark
Magnus Guldberg Pedersen is a machine learning researcher and
engineer at BrainCapture ApS, a Danish medtech start-up making
EEG-based diagnosis of neurological disorders available where
specialist expertise is scarce. He builds foundation models
and automated diagnostic pipelines for clinical EEG and took
part in the second round of the Danish regulatory sandbox for
AI. He is also a research engineer at DTU and
Rigshospitalet.
Parallel workshop session 1 — choose one
Relative identifiability in health data: pseudonymisation and secondary use governance
Where does pseudonymised data stop being personal data? A panel on re-identification risk, defensible thresholds and the governance that makes secondary use workable.
 Panellist
Khaled El Emam,
University of Ottawa
Canada Research Chair in Medical AI; Professor, School of
Epidemiology and Public Health
Canada
Dr. Khaled El Emam is the Canada Research Chair (Tier 1)
in Medical AI at the University of Ottawa, where he is a
Professor in the School of Epidemiology and Public Health.
He is also a Senior Scientist at the Children's Hospital
of Eastern Ontario Research Institute, and in 2024-2025
was the Scholar-in-Residence at the Office of the
Information and Privacy Commissioner of Ontario (IPC).
Khaled has founded or co-founded eight product and
services companies involved with data management and data
analytics, with some having successful exits. Prior to his
academic roles, he was a Senior Research Officer at the
National Research Council of Canada. He also served as the
head of the Quantitative Methods Group at the Fraunhofer
Institute in Kaiserslautern, Germany. He has a PhD from
the Department of Electrical and Electronics Engineering,
King's College, at the University of London,
England.
 Panellist
Sophie Stalla-Bourdillon,
Brussels Privacy Hub, VUB
Co-Director
Belgium
Sophie is Co-Director of the Brussels Privacy Hub at
Vrije Universiteit Brussel. She previously held the Chair
in IT Law and Data Governance at the University of
Southampton and led the Legal Engineering team at Immuta,
working on data operations, analytics, AI and compliance
automation.
Chair
Winnie Dongbou Wamba,
MyData-TRUST
Transformation Lead & Senior Data Protection
Lawyer
Belgium
Winnie Dongbou Wamba is a senior data protection lawyer
specialising in the life sciences sector, with experience
advising on global privacy, health data research and
cross-border data transfer matters. He is currently
pursuing a PhD in law on the legal and ethical challenges
of synthetic data in research, with a particular focus on
clinical research and the European Health Data Space. His
work sits at the intersection of data protection, medical
law, emerging technologies and research ethics.
Connected glasses in care and at work
Smart glasses are moving from pilot to ward. A roundtable between platform, industry and hospital privacy leads on capture, consent and the boundary between clinical benefit and surveillance.
 Chair
Daniela Will,
München Klinik
DPO and Head of the Data Protection Unit
Germany
Daniela Will is a Certified Data Protection Officer
(TÜV®), Data Protection Auditor DSA-TÜV, GDDcert.EU and
Certified Information Privacy Professional/Europe
(CIPP/E). She heads the GDD-ERFA-Kreis Bayern as well as
the VBW Arbeitskreis Datenschutz and lectures on data
protection law at the Hochschule Aalen. Daniela draws her
knowledge from over 30 years of professional experience in
various areas of the IT, automotive and media industries
and has many years of in-depth knowledge in the field of
data protection. Since June 2024, she is head of the data
protection department at München Klinik gGmbH. Her
questions regularly centre on the establishment and
management of an agile, maturity-oriented data protection
organisation based on IDW 9.860.1, the legal enabling of
the use of patient data in medical research projects, and,
of course, the EHDS.
 Speaker
Aleksandra Aytova,
Applegreen
Group Head of Privacy
Ireland
Dr. Aleksandra Aytova is the Group Head of Privacy and AI
Governance at Applegreen and an internationally recognised
expert in human rights, digital ethics, and technology
law. With over 15 years of legal and corporate leadership
experience, she helps organisations navigate the
intersection of innovation, regulation, and risk. Dr.
Aytova holds a Ph.D. in Fundamental Rights from Sofia
University, a Master’s in IT Law from Tartu
University, and a specialisation in AI and Machine
Learning from MIT. A passionate advocate for responsible
innovation, her work focuses on safeguarding human rights
and advancing ethical AI-assisted decision-making in the
digital age.
 Speaker
Georgia Voudoulaki,
Bosch
Senior Legal Counsel
Germany
Georgia Voudoulaki is an attorney-at-law and Senior
Legal Counsel at Robert Bosch GmbH in Stuttgart,
specialising in data protection, AI governance and
digital transformation. A certified AI Officer and
Compliance Officer, she translates AI regulatory
requirements into practical governance structures,
responsibilities and business processes. She is also a
university lecturer, legal author and speaker on AI
governance, data protection and cybersecurity, and a
member of the European Data Protection Board's Support
Pool of Experts.
 Speaker
Cecilia Álvarez Rigaudias,
Meta
Director of Data and Privacy Policy, Europe
Spain
Cecilia Álvarez Rigaudias has led privacy policy
for Meta in Europe since 2019. She previously served as
European Privacy Officer Lead at Pfizer and spent 18 years
in private practice leading data protection, IT,
e-commerce and Latin American privacy work.
Parallel workshop session 2 — choose one
Tokenisation: privacy by design for medical research
How tokenisation lets research datasets be linked across sources without moving identifiers — and what regulators expect from the key management around it.
 Chair
Anne Bahr,
Sanofi
R&D Privacy Officer
France
Anne Bahr is R&D Privacy Officer in Sanofi’s
Global Privacy Office. She supports research and
development projects involving health data, including
real-world data studies, registries, managed access
programmes, patient support programmes and data
foundations. Her earlier work covered worldwide clinical
studies and international R&D projects, with a focus
on patient consent, ethics review, biological samples,
secondary use and anonymisation. She represents Sanofi in
the EFPIA Data Governance Working Group, is CIPP/E
certified and holds a PhD in Molecular Biology.
Speaker
Khaled El Emam,
University of Ottawa
Canada Research Chair in Medical AI; Professor, School of
Epidemiology and Public Health
Canada
Dr. Khaled El Emam is the Canada Research Chair (Tier 1)
in Medical AI at the University of Ottawa, where he is a
Professor in the School of Epidemiology and Public Health.
He is also a Senior Scientist at the Children's Hospital
of Eastern Ontario Research Institute, and in 2024-2025
was the Scholar-in-Residence at the Office of the
Information and Privacy Commissioner of Ontario (IPC).
Khaled has founded or co-founded eight product and
services companies involved with data management and data
analytics, with some having successful exits. Prior to his
academic roles, he was a Senior Research Officer at the
National Research Council of Canada. He also served as the
head of the Quantitative Methods Group at the Fraunhofer
Institute in Kaiserslautern, Germany. He has a PhD from
the Department of Electrical and Electronics Engineering,
King's College, at the University of London,
England.
 Speaker
Erik Boucher de Crèvecoeur,
CNIL
Senior health expert engineer
France
Erik Boucher de Crèvecoeur is an information
technology expert at the CNIL. With nearly 30 years of
experience in software development, quality and security
management, he works on compliance checks for personal
data processing in the French health sector and
contributes to national frameworks and international
privacy standards.
Impact of new technology in health data protection: neuroprivacy
Brain–computer interfaces and care robotics generate categories of data that existing frameworks were never written for. This workshop examines what governance for neural and behavioural data should look like.
 Chair
Ahmed Alhatlan,
Gulf Center for Disease Prevention and Control
Data Governance and Policy Manager · JHDP
Editorial Board
Saudi Arabia
Ahmed Alhatlan is a digital public health and health data
governance specialist with more than 20 years of
experience across government, private and non-profit
organisations. He is Data Governance and Policy Manager at
the Gulf CDC, Vice President of the Saudi Health
Information Management Association and IFHIMA Regional
Director for the Eastern Mediterranean.
 Speaker
Baroum Mrad,
Ente Ospedaliero Cantonale
Chief Privacy & Compliance Officer; Head of Data
Protection & Compliance
Switzerland
Baroum Mrad is the Chief Privacy and Compliance Officer
(CPCO) and Head of the Data Protection & Compliance
Department at the Ente Ospedaliero Cantonale (EOC) -
Healthcare System of South of Switzerland. He is an expert
in compliance and privacy, with particular expertise in
neuroprivacy, brain-computer interfaces (BCI), and
healthcare. He has a diverse background in business, data
science engineering, and law, and with 20 years of
experience in data science and privacy—particularly in the
healthcare sector—he has effectively navigated the
complexities of technology, strategy, and data protection.
His expertise lies at the intersection of legal and
technological aspects of healthcare, making him a unique
asset in the industry. He is the author of the Springer
book Healthcare Services Management: A Practical
Guide.
 Speaker
Matthieu Lequesne
CNIL
PhD, scientific expert · Personal data protection
· Post-quantum cryptography · Health data
regulation · Transparency and accountability
France
Dr Matthieu Lequesne is a scientific expert at the CNIL. His work spans personal data protection, post-quantum cryptography, health data regulation, transparency and accountability.
Parallel workshop session 3 — choose one
Genomic data and biobanks in the EHDS era
Genetic data presents some of the most complex legal, ethical and operational challenges in healthcare. This workshop looks at governance frameworks, research opportunities and the safeguards needed for responsible use of genomic information.
 Chair
Tania Palmariello Diviney
Data Privacy Simplified
Founder & CEO; Data Protection Officer
United Kingdom
Tania Palmariello Diviney is the Founder and CEO of Data Privacy Simplified, Co-founder and Director of The Privacy Centre, and Co-founder of HumanLoop AI. An information governance and data protection specialist, she has worked across health and social care, education, research and innovation, including with NHS England. She holds a Master’s in Health Information Governance and regularly speaks on privacy, cyber risk, ethical data use and responsible innovation.
 Speaker
Laura Centeno Casado,
CSIC
PhD Researcher, Applied Ethics Research Group
Spain
Laura Centeno Casado is a PhD researcher at the Institute
of Philosophy of the Spanish National Research Council
(CSIC). Her work examines bioethics, health data, digital
health, artificial intelligence and the governance of the
European Health Data Space.
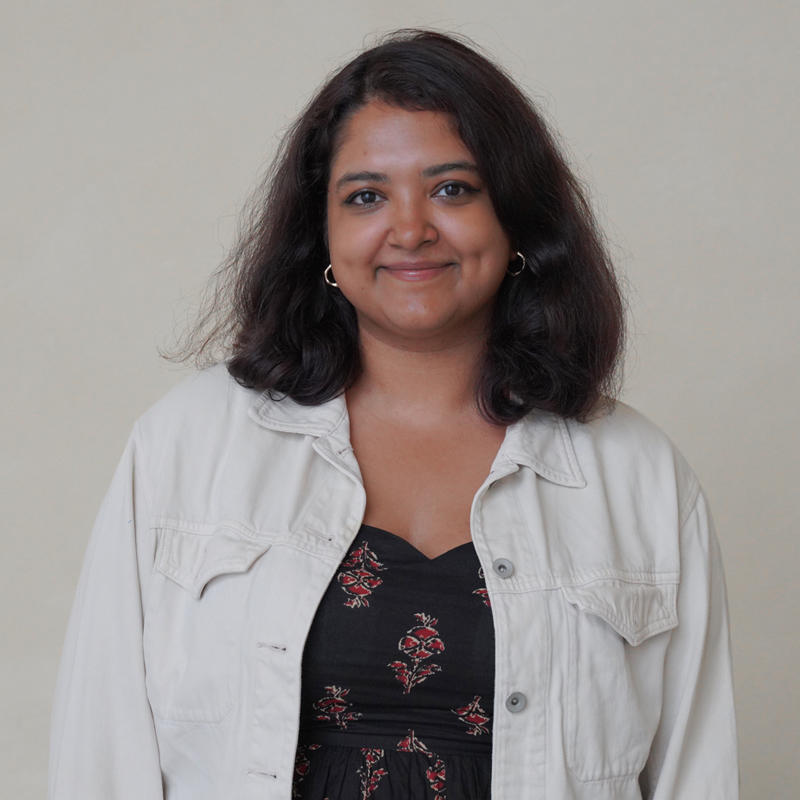 Speaker
Anamika Kundu,
European University Institute
PhD Researcher, Law Department
Italy
Anamika Kundu is a PhD researcher at the Law Department of
the European University Institute in Italy. Her research
examines the socio-legal implications of the European
Health Data Space Regulation, including how it reshapes
power relations among healthcare actors and what the
broader framework means for agency, public interest and
data quality.
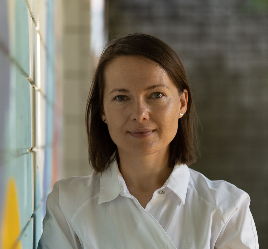 Speaker
Lina Jasmontaite,
UDG Alliance
Researcher & Project Manager
Switzerland
Lina Jasmontaite is a researcher and project manager at
UDG Alliance, contributing to large-scale EU-funded
projects at the intersection of healthcare and digital
innovation. She coordinates work on legal, ethical and
policy aspects and publishes on personal data protection,
human rights, emerging technologies and awareness of
privacy rights.
Cybersecurity and health data protection
Cybersecurity incidents increasingly affect healthcare organisations and critical infrastructures. Participants will discuss resilience strategies, incident management, NIS 2 requirements and practical approaches to strengthening organisational security.
 Chair
Daniela Will,
München Klinik
DPO and Head of the Data Protection Unit
Germany
Daniela Will is a Certified Data Protection Officer
(TÜV®), Data Protection Auditor DSA-TÜV, GDDcert.EU and
Certified Information Privacy Professional/Europe (CIPP/E).
She has more than 30 years of professional experience and
has headed the data protection department at München
Klinik since June 2024. Her work includes enabling the use
of patient data in medical research projects and preparing
for the EHDS.
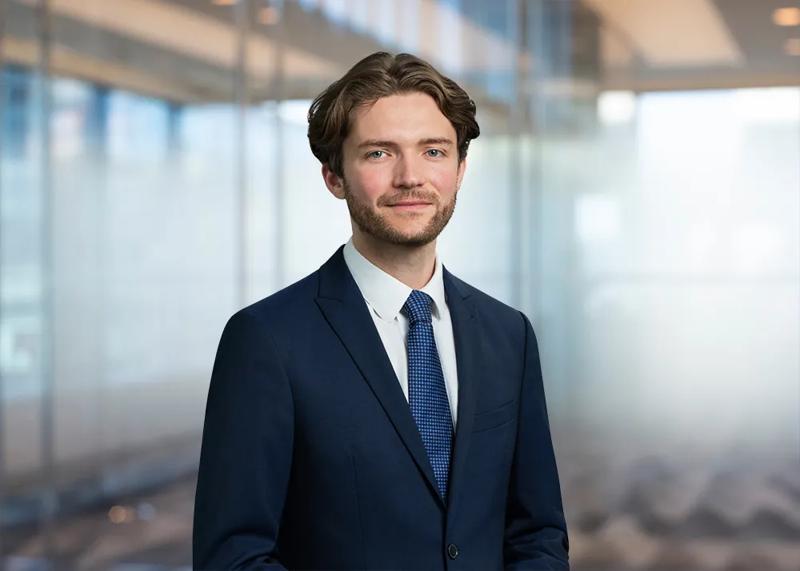 Speaker
David Brazil,
Covington & Burling LLP
Associate
Belgium
David Brazil is an associate in Covington’s Data
Privacy and Cybersecurity Practice Group, based in Brussels.
He advises clients on European regulations related to
technology and cybersecurity, including the GDPR, AI Act,
DORA, Cyber Resilience Act and NIS 2.
 Speaker
Gauthier Bencheïkh,
FTI Consulting
Senior Director, Strategic Communications
France
Gauthier Bencheïkh is a Senior Director at FTI
Consulting, serving as a strategic adviser and operational
lead on crisis communications and corporate media relations.
He has 11 years of experience supporting public- and
private-sector clients through growth, transformation and
critical situations. His healthcare work includes
engagements for the ANSM, Ergéa, PTC Therapeutics,
SERB Pharmaceuticals, Servier, Stallergenes Greer and
Synlab, as well as crisis communications related to
cyberattacks and other sensitive matters.
Parallel workshop session 4 — choose one
Medical digital twins and synthetic data
Synthetic cohorts and patient digital twins promise research value without exposing real records. The panel tests that promise against re-identification risk, validity and regulatory acceptance.
 Chair
Cécile Théard-Jallu,
De Gaulle Fleurance
Partner
France
Cécile Théard-Jallu is a partner at De
Gaulle Fleurance specialising in innovation, digital
technology, cybersecurity, data privacy, healthcare and
life sciences. She advises on regulatory compliance,
clinical research, telemedicine, artificial intelligence,
digital twins and primary and secondary uses of health
data.
 Panellist
Jean-Louis Fraysse,
BOTdesign · INeS · SoFIA-Santé
Co-Founder of BOTdesign; Vice-President of INeS &
SoFIA-Santé
France
Jean-Louis Fraysse is a digital-health expert and
co-founder of BOTdesign, which develops AI solutions for
healthcare and clinical research. He is also
Vice-President and Think Tank Coordinator of INeS and
Vice-President of SoFIA-Santé, where he supports
professionals and institutions working on AI in health,
including medical digital twins.
 Panellist
Emmanuel Pham,
Nova In Silico
Senior Vice President, Science & Customer Experience
Europe
Emmanuel Pham has more than 20 years of experience across
the pharmaceutical industry and academia. At Nova In
Silico, he works on mechanistic modelling, digital twins,
virtual patient populations and in silico clinical trials,
and helps pharmaceutical companies and regulators
integrate clinical-simulation evidence into development
programmes and regulatory submissions. He is also a board
member of EFSPI and ARIIS.
 Panellist
Isabelle Landreau,
IDEMIA
Attorney and Group DPO
France
Isabelle Landreau is a technology-focused attorney and IT
mediator with more than 18 years of legal experience. She
serves as Group Data Protection Officer at IDEMIA and
teaches digital-contract and health-data law at Paris II
and ESSEC. Her work covers GDPR, cybersecurity and the
regulatory dimensions of digital innovation.
From lab to launch: data protection in bringing new medical devices to market
This session explores the range of data protection issues to consider when designing, testing and commercialising new medical devices — and how those issues shift from one device type to another, from implantables to capital equipment to consumer wearables.
 Chair
Peter A. Blenkinsop,
Faegre Drinker
Lawyer
United States
Peter Blenkinsop is a Partner at Faegre Drinker Biddle
& Reath LLP and leads the firm’s Privacy,
Cybersecurity, Data Ethics & Strategy practice. He has
more than 20 years of experience advising companies on
privacy and data protection compliance, including many of
the world’s leading pharmaceutical and medical
device companies. His work includes programme assessments,
compliance advice and the development of data protection
programmes. He also supports the International
Pharmaceutical and Medical Device Privacy Consortium and
the Diagnostics Privacy Consortium.
 Panellist
Océane Bayrou,
GE HealthCare
Executive Counsel & Deputy Privacy Officer
France
Océane Bayrou is a privacy and data protection
lawyer advising on the legal, regulatory and governance
aspects of digital health, health data and artificial
intelligence. At GE HealthCare, she supports global
privacy and data protection initiatives and helps navigate
the complex regulatory frameworks that shape the
development and deployment of innovative healthcare
technologies. Her experience spans privacy governance,
compliance and the responsible use of data in
healthcare.
 Panellist
Efstathia Gkika
Legal, Compliance & Privacy Advisor; former Global
Chief Privacy Officer, Baxter International
Switzerland
Efstathia (Efi) Gkika is a multi-lingual lawyer who started her
career with an international law firm of one of the Big
Four. For the last 18+ years she has been dedicated to the
pharma/medical devices sector in Legal/Compliance and Data
Privacy roles having worked for Roche and Novartis in
various regional and global positions, and served also at
the role of the Deputy General Counsel and Global Chief
Privacy Officer of Baxter International. Throughout her
career Efi has been acting as a strategic partner of the
C-Suite and the global and regional stakeholders
supporting both privacy compliance, AI, digital
transformation, digital health, connected care and M&A
matters from the privacy side. She held the position of
the Chair of MedTech Europe Privacy Committee. Efi studied
law in the University of Athens in Greece and holds an LLM
from the Université libre de Bruxelles in European Law and
an LLM from the Economic University of Athens in
International Business Taxation. She has also completed a
course on Digital Disruption, Digital Transformation with
the Cambridge Judge Business School, has attended the IAPP
AI Governance training and the ETH course on AI and Health
Data. Recently Efi completed the Digital and AI
Transformation course with the IMD.
 Panellist
Mirella Kavadaki,
MedTech Europe
Manager Legal & Compliance
Belgium
Mirella Kavadaki is a qualified lawyer and Manager for
Legal & Compliance and Legal Counsel at MedTech
Europe, the European trade association representing the
medical technology industry. She leads the
organisation’s work on data protection and privacy,
with a particular focus on health data processing and the
interaction between the GDPR, EU digital legislation and
medical device regulation. Mirella holds an Advanced LL.M.
in Intellectual Property & ICT Law from KU Leuven and
an MSc in European Public Law from Panteion University of
Social and Political Sciences.
Striking the right balance: don’t throw the baby out with the bath water
Ensuring privacy regulation achieves its purpose without holding back innovation and treatment
This session brings together privacy leaders in the life sciences industry and data protection authorities to consider the evolving regulatory landscape, including EU regulations such as the EHDS, the AI Act, the GDPR and MDR/IVDR. Panellists will address regulatory complexity, and how companies and regulators can partner to achieve shared goals by building trust and enabling responsible data use.
Industry leaders will also discuss why internal partnerships with senior management and IT leaders are essential in navigating regulatory requirements while committing to a strategy that embraces innovation and competition. Panellists will share lessons learned, including case studies from the pharmaceutical and medical technology industries where regulation either created barriers to treatment and best practice, or achieved a healthy balance.
 Chair
Mary Devlin Capizzi,
Faegre Drinker
Partner
United States
Mary Devlin Capizzi is a partner at the law firm of Faegre
Drinker Biddle & Reath and based in Washington, DC. Mary
has nearly three decades of experience building relationships
at the intersection of law, regulation, science, and policy,
advising pharmaceutical, biotechnology, medical device, and
consumer health clients on complex compliance, legislative,
scientific, and agency-facing matters. She currently serves
Faegre Drinker as the leader of its global life sciences
consortia management team and has held numerous firm
leadership roles over her career, including as a longtime firm
Board member, an executive partner, and co-leader of the
firm’s health and life sciences sector. For almost 30
years, Mary has partnered with industry leaders to establish
and operate pre-competitive collaborative initiatives on a
wide range of topics, including data governance, cyber
security, AI and federated learning, innovation in drug
development, supply chain security, patient safety, product
quality, clinical trials, and data sharing. Mary enjoys
solving complex problems collaboratively. She and the
consortia management team proactively align industry leaders
around shared goals, maintain rigorous, efficient coordination
among stakeholders, and build and sustain trust to ensure
flourishing of industry initiatives and achieving identified
objectives. Mary, along with her colleague, Peter Blenkinsop,
worked with global industry leaders to establish the
International Pharmaceutical and Medical Device Privacy
Consortium (IPMPC) in 2001–2002. Mary received her law
degree from Emory University School of Law in Atlanta,
Georgia, her BA, and MBA from the University of Dallas, in
Irving, Texas. She is a fluent Spanish speaker who has lived
and worked in Spain, France, Italy and Mexico.
 Panellist
Dorotea Alessandra De Marco,
Garante (Italian DPA)
Senior Officer, Digital Technologies & IT Security
Italy
Dorotea Alessandra de Marco Senior official at the Italian
Data Protection Authority since 2014 within the Digital
technology and IT security department. Her role includes
providing technical consultancy to the legal Departments
regarding complaints, inspections on lawfulness and security
measures of data processing, data breaches, prescriptions and
opinions with a focus on personal data protection in the
health sector. She is in charge of any activity related to
accreditation, certification and code of conduct under the
GDPR. She has been appointed expert in the international,
european and national standardization bodies (ISO/IEC JTC 1/SC
27/WG 5 “Information technology - Security techniques -
Identity management and privacy technologies”, former ISO PC
317 “Consumer protection - Privacy by design for consumer
goods and services”, CEN/CENELEC JTC 13/WG5 “Privacy
management in products and services”) and she is also involved
in the development of many privacy standards. She worked for
the Ministry of Health, IT Division (2004-2013), Ministry of
Economic Development, IT division (2000-2004) and Telecom
Italia, Network Division (1995-2000). She is an electronic
engineer and graduated at “Tor Vergata” University of Rome,
she also achieved a Master's Degree in Telecommunications from
the High School of Specialization in Telecommunications.
 Panellist
Noemí Alonso Calvo,
Takeda
Lead Counsel, Data Protection & AI Trust
Spain
Noemí Alonso Calvo is a Spanish-qualified lawyer with
more than 20 years of privacy experience across life sciences,
technology, consumer products and banking. She is Lead
Counsel, Data Protection & AI Trust at Takeda and has held
senior privacy roles at Johnson & Johnson, Novartis,
Deliveroo, bluebird bio, UBS, AbbVie and NAC Privacy Global.
She holds the CIPP/E and CCEP-I certifications and is a
Co-Chair of the Cambridge Forum on International Privacy &
Data Laws.
 Panellist
Dr Pascal Hofer,
Roche
Head of Legal Digital and IT · Attorney at Law
Switzerland
Dr Pascal Hofer is Roche Head of Legal Digital and IT and an
attorney at law. He leads the implementation of key digital
and data legislation across the group, including the EU AI
Act, Data Act and EHDS Regulation, with a focus on their
impact on healthcare companies and advanced medical
technologies.
 Panellist
Igor Versteeg,
Opella Healthcare
Global Privacy Operations Lead · DPO for Opella France
& Germany · Science Hub Privacy Partner
France
Igor Versteeg is a data protection officer and legal project
manager with a strong interest in information technology. He
leads privacy operations at Opella Healthcare, serves as DPO
for its France and Germany operations, and is its Science Hub
Privacy Partner. His work includes privacy governance, risk
management, digital transformation, audit and EU AI Act
readiness.
Day 3 — Friday 16 October 2026
From regulation to implementation
EHDS: an unfolding story — the DPO perspective
With implementation approaching, organisations across Europe are asking the same question: are we truly ready for the European Health Data Space?
The European Commission speaker will give a reminder of the current situation and an update on the latest developments. Together with health data holders, health data users from academia and the life sciences, and patient representatives, the session will assess implementation progress, operational readiness and the challenges facing healthcare institutions.
 Chair
Dipak Kalra,
i~HD
President
United Kingdom
Professor Dipak Kalra is President of The European Institute
for Innovation through Health Data. He plays a leading
international role in electronic health record research and
development, including the reuse of EHRs for research, and has
led ISO standards work on EHR interoperability, personal
health records and data protection. He contributes to several
European Commission-funded projects on digital health
innovation, health data quality and interoperability, the
European Health Data Space, value-based care, federated
learning in lung cancer and medication adherence.
 Speaker
Guillaume Byk,
European Commission · DG Health
Legal and Policy Officer · Unit C1 Digital
Health
Belgium
Guillaume Byk is a legal and policy officer at the European
Commission, DG Health, Unit C1 on Digital Health. He is a
lawyer specialised in data protection and biomedical law.
Prior to joining DG Health, Guillaume worked at the office of
the European Data Protection Supervisor and at the national
data protection authority of Luxembourg on the implementation
of the GDPR. Previously, he worked for more than 10 years as a
data protection officer and legal counsel in a public
biomedical research centre in Luxembourg.
 Speaker
Yacine Daquin,
Health Data Hub
Head of Legal
France
Yacine Daquin is the Health Data Hub's head of legal. He is
in charge of legal matters relating to the secondary use of
healthcare data, both at national and European level. In
particular, he supports the Health Data Hub's activities in
prefiguring and preparing for the future European health data
space. Previously, he pursued a PhD on the regulation of
artificial intelligence in healthcare, investigating the legal
and ethical issues associated with the design and deployment
of these systems.
 Speaker
Dr Sofia Tsekeridou,
Netcompany
Senior Research & Innovation Manager
Greece
Dr Sofia Tsekeridou is a Senior Research and Innovation
Manager – Expert in Netcompany’s Research and
Innovation Development Department. She holds an ECE diploma
and a PhD in Computer Science from Aristotle University of
Thessaloniki. Her work spans project and technical management,
software engineering, multimodal data management, artificial
intelligence and cybersecurity. She is a senior IEEE member,
co-leads the BDVA Healthcare Task Force and is an expert
member of the FCT-INFRA subgroup of the European
Commission’s DG HOME CERIS expert group.
 Speaker
Yann Heyer,
European Patients’ Forum
Policy Officer
Belgium
In his role as Policy Officer, Yann contributes to
EPF’s policy and advocacy work, including formulating
positions in consultation with patient organisations and
engaging with external stakeholders. He covers mainly topics
such as digital health and artificial intelligence. Yann is
Franco-German and holds a Franco-German degree from Sciences
Po Lille and the University of Münster.
Speaker
Daniela Will,
München Klinik
DPO and Head of the Data Protection Unit
Germany
Daniela Will is a Certified Data Protection Officer
(TÜV®), Data Protection Auditor DSA-TÜV, GDDcert.EU and
Certified Information Privacy Professional/Europe (CIPP/E).
She has more than 30 years of professional experience across
the IT, automotive and media industries and has headed the data
protection department at München Klinik since June 2024.
Her work includes enabling the use of patient data in medical
research projects and preparing for the EHDS.
Becoming EHDS ready: the operational roadmap
A European Commission update on the implementing acts and on progress across Member States, followed by a panel on what it actually takes to deliver.
Speakers each take a different perspective on one question: how should a DPO help their organisation get EHDS ready?
- Meeting the primary use obligations
- Acting as a data holder
- Acting as a data user
- Responding to the new rights of patients
Panel discussion: what operational steps deliver on the EHR obligations, what are the capacity-building challenges, and how can the costs be met?
 Chair
Nathan Lea,
i~HD
Information Governance Lead and Data Protection Officer
United Kingdom
Dr Nathan Lea is an independent consultant working with i~HD
as Data Protection Officer and Information Governance Lead. He
applies data protection, ethics and therapeutic-relationship
principles to ambitious multiparty and multinational
innovation programmes. He leads the development of adaptive
codes of practice and operating procedures for the secure use
of health data in care, research and digital health
innovation, with a particular interest in artificial
intelligence and emerging regulation. He has more than twenty
years of digital health experience, including roles at Cancer
Research UK and UCLH NHS Foundation Trust, and a background in
medical informatics, software engineering and academic
research at UCL.
Speaker
Dr Sofia Tsekeridou,
Netcompany
Senior Research & Innovation Manager
Greece
Dr Sofia Tsekeridou is a Senior Research and Innovation
Manager – Expert in Netcompany’s Research and
Innovation Development Department. She holds an ECE diploma
and a PhD in Computer Science from Aristotle University of
Thessaloniki. Her work spans project and technical management,
software engineering, multimodal data management, artificial
intelligence and cybersecurity. She is a senior IEEE member,
co-leads the BDVA Healthcare Task Force and is an expert
member of the FCT-INFRA subgroup of the European
Commission’s DG HOME CERIS expert group.
 Speaker
Louise Manchon,
CNIL
EHDS and health data specialist
France
Louise Manchon is a lawyer at the CNIL whose work focuses on
health data and the European Health Data Space. She
contributes to the authority’s guidance and outreach on
the secondary use of health data and patients’
rights.
Speaker
Yann Heyer,
European Patients’ Forum
Policy Officer
Belgium
Yann Heyer contributes to the European Patients’
Forum’s policy and advocacy work, including positions
developed with patient organisations. His main topics include
digital health and artificial intelligence.
 Speaker
Yacine Daquin,
Health Data Hub
Head of Legal
France
Yacine Daquin is Head of Legal at the Health Data Hub. He
advises on the secondary use of health data at national and
European level and supports preparation for the European
Health Data Space.
Speaker
Daniela Will,
München Klinik
DPO and Head of the Data Protection Unit
Germany
Daniela Will is a Certified Data Protection Officer
(TÜV®), Data Protection Auditor DSA-TÜV, GDDcert.EU and
Certified Information Privacy Professional/Europe (CIPP/E).
She has more than 30 years of professional experience across
the IT, automotive and media industries and has headed the data
protection department at München Klinik since June 2024.
Her work includes enabling the use of patient data in medical
research projects and preparing for the EHDS.
Artificial intelligence, global health data governance and the future of healthcare
A forward-looking keynote examining how AI, health data governance and international cooperation will shape healthcare systems over the next decade.
 Keynote
Eric Sutherland,
OECD
Senior Health Economist, Digital Health
France
Eric is a Senior Health Economist leading the OECD’s work in
Digitalisation of Health, bringing together policy guidance
for digital security, integrated data, and responsible
analytics including artificial intelligence. In that role, he
is accountable for measuring and evolving the OECD’s
Recommendation on Health Data Governance (2016) and supporting
policy for digitalisation of health that provides data
protection (e.g. security and privacy) and timely access to
quality data to optimize the use of data for information,
insights, and impact among individuals, health workers, policy
makers, researchers, and innovators.
Congress closing
Closing remarks from the EHDPC co-chairs.
 EHDPC Co-chair
Pierre-Yves Lastic,
EFDPO / EHDPC
Secretary General
France
Pierre-Yves Lastic is Secretary General of EFDPO and EHDPC
Co-chair. He has extensive experience in data governance,
privacy and the life sciences sector.
 EHDPC Co-chair
Dipak Kalra,
i~HD / EHDPC
President, i~HD
United Kingdom
Professor Dipak Kalra is President of the European Institute
for Innovation through Health Data and EHDPC Co-chair. He plays
a leading international role in health-data research,
interoperability and responsible data use.
Who should attend
- Data Protection Officers
- Chief Data Officers
- Privacy professionals
- Compliance officers
- Digital health leaders
- Healthcare providers
- Hospitals and university hospitals
- Pharmaceutical and biotech companies
- Medical device manufacturers
- Researchers and academic institutions
- Health data access bodies
- Regulators and supervisory authorities
- EHDS implementation project managers
- AI governance and risk professionals
2026 key themes
- European Health Data Space
- Artificial intelligence and health data
- Health data governance
- Scientific research
- Secondary use of health data
- Cybersecurity and resilience
- Medical devices
- Genetic and genomic data
- Data protection compliance
- International data transfers
- Emerging technologies
- Operational readiness and capacity building
Sessions, timings and speakers may change.